A company gets acquired. Six months after close, the acquirer discovers the target had a breach two years earlier that was never disclosed. Or that the entire customer database is sitting in a misconfigured cloud bucket. Or that the IT environment is held together by one contractor’s tribal knowledge and nothing else.
This happens more than people think. Standard due diligence covers financials, contracts, IP, employment. Cyber gets a checkbox. That’s how deals get repriced after close.
What standard diligence misses
Most M&A diligence runs a security questionnaire past the target. They fill it out. Everyone moves on. The problem is that questionnaires capture what the target says, not what’s actually true. A target can answer “yes, we have MFA” because they have it on one system. The other twelve, no.
The other miss is undisclosed incidents. A breach two years ago that nobody told regulators about — and nobody is going to tell you about. That liability transfers to the acquirer at close.
Integration risk
Post-close, the target’s environment connects to yours. Everything they bring in — vulnerabilities, dormant accounts, weak controls — becomes your problem. Mapping that integration risk before close is what separates clean integrations from painful ones.
Why this matters for PE specifically
For private equity, this isn’t a one-off deal concern. It’s a portfolio question. Every acquisition adds environments, and the aggregate posture of the portfolio is what determines exposure at the fund level.
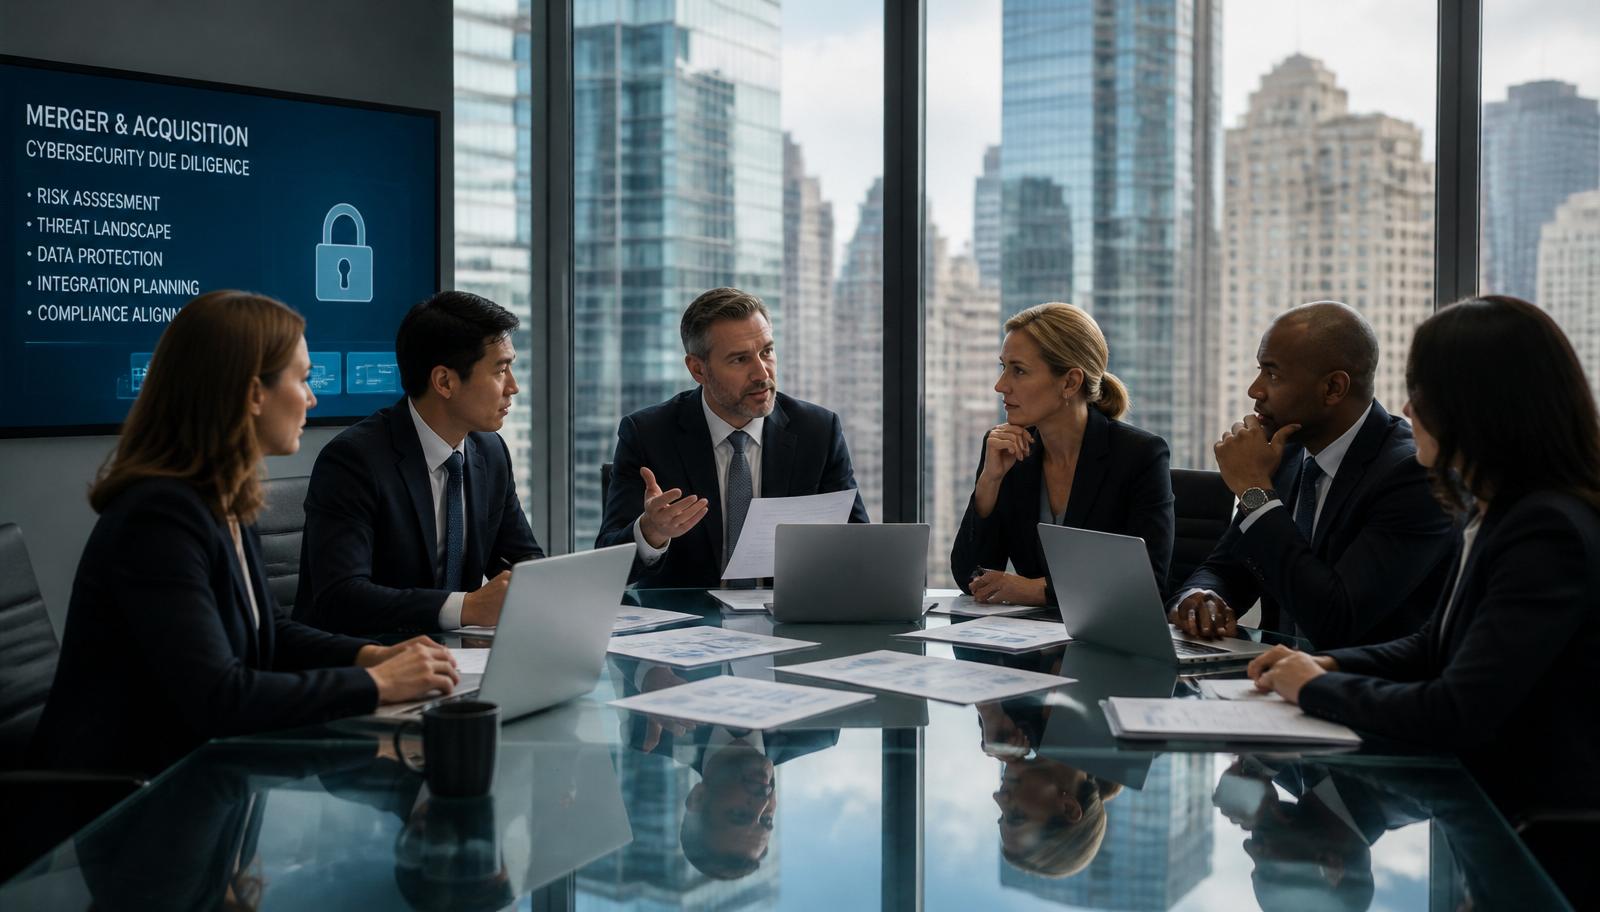
A structured cyber due diligence for M&A engagement looks at each deal individually and how it fits into the broader portfolio standard.
What changes when diligence catches something
The deal doesn’t have to die. It usually gets repriced or restructured. The acquirer asks for representations and warranties around cyber. The target funds remediation pre-close or post-close at their expense. Specific risks get carve-outs.
What doesn’t happen — when diligence is done right — is the acquirer absorbing a breach disclosure six months in and finding out it was knowable beforehand.
Bottom line
Cyber due diligence is no longer optional. The cost of doing it is small relative to the deal. The cost of not doing it shows up in repriced earnouts, regulatory action, and integration nightmares that take years to unwind.
Defensible runs cyber diligence for PE firms and strategic acquirers so deals close with eyes open. Talk to an expert.