You can have an incident response plan that looks great on paper and falls apart the moment a real incident hits. The only way to know which one you have is to test it. That’s what a tabletop exercise does.
What a tabletop actually is
It’s a simulation. A scenario gets dropped on the team — ransomware on a critical server, a data exfiltration alert, a CEO impersonation fraud — and the team works through how they’d respond. Nobody touches a system. Nobody pulls a cable. They talk through it. Who does what, in what order, with what information.
The goal isn’t to grade people. It’s to find the gaps. Almost every tabletop reveals something. A contact list that’s out of date. A decision nobody knows who owns. A vendor whose phone number is buried in an old email.
Who needs to be in the room
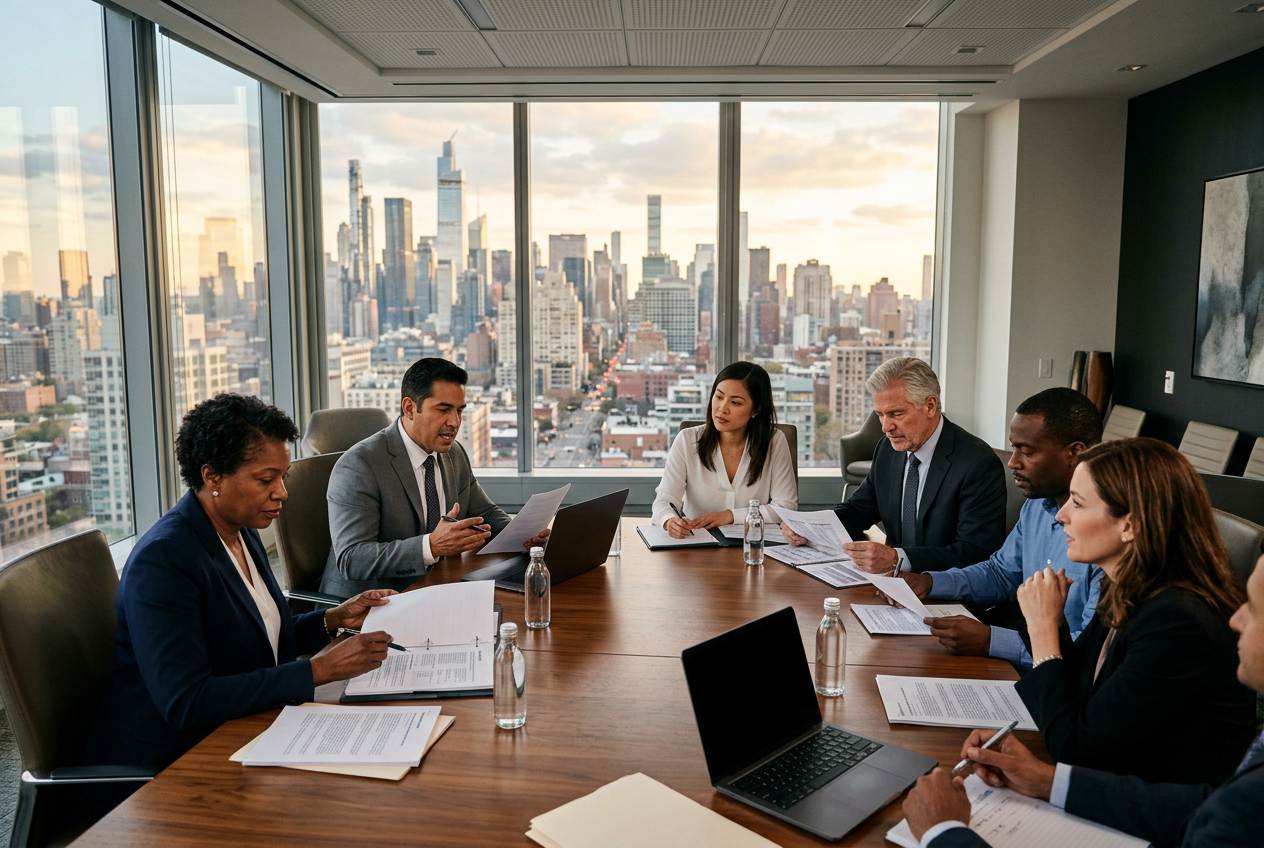
This is where SMBs get it wrong. They run a tabletop with just IT. That’s not enough. A real incident pulls in legal, finance, communications, the executive team, and sometimes HR. If those people first meet during the actual incident, you’ve already lost time.
Bring the executive team. Bring whoever handles communications, internal and external. Bring legal if you have counsel. Bring the IT lead and whoever owns the relationship with your incident response provider. If a customer-facing role would be involved in the response, bring them too.
How to structure it
A good tabletop runs 60 to 120 minutes. Longer than that and people zone out. Shorter and you don’t get past the obvious.
A facilitator sets the scenario and adds injects — new information that changes the situation. “Two hours in, you discover the attacker also accessed your customer database.” “Your IT provider is unreachable for the first 30 minutes.”
What to look for during the exercise
Watch for hesitation. If people don’t know who makes a decision, that’s a gap. Watch for assumptions. “IT will handle that” — will they? On a Sunday night? Watch for information gaps. Who has the cyber insurance policy number? Who calls the bank? Who notifies customers, and what do they say?
The exercise isn’t successful when nobody stumbles. It’s successful when the stumbles become a list.
What happens after
This is the part most SMBs skip. The tabletop ends, everyone goes back to work, the lessons evaporate. Don’t do that.
The output of a tabletop should be a short document. What worked. What didn’t. What changes get made, by whom, by when. Then revisit it before the next exercise.
For organizations serious about response readiness, this kind of exercise should connect to broader incident response and digital forensics planning — not as a standalone event, but as part of how the program stays sharp.
Frequency
Once a year minimum. Twice if your environment changes a lot or you’re in a regulated industry. The first one will be rough. The second one will be sharper. By the third one, the team operates differently — they know each other, they know the plan, they don’t panic.
Defensible runs tabletop exercises with SMBs to find the gaps before attackers do. Talk to an expert.