Most fraud attacks used to rely on one thing: urgency.
A rushed wire transfer. A panicked executive email. A fake invoice sent at the wrong moment.
AI has changed the scale and sophistication of those attacks entirely.
Today, attackers can clone a CEO’s voice, generate realistic video calls, mimic internal communication patterns, and create convincing executive impersonation fraud campaigns that bypass the instincts employees once relied on.
For SMBs, that changes the risk model significantly. Because the attack no longer looks suspicious.
What Deepfake CEO Fraud Actually Looks Like
Most people imagine deepfakes as obvious fake videos on social media. That’s not how these attacks usually happen inside businesses.
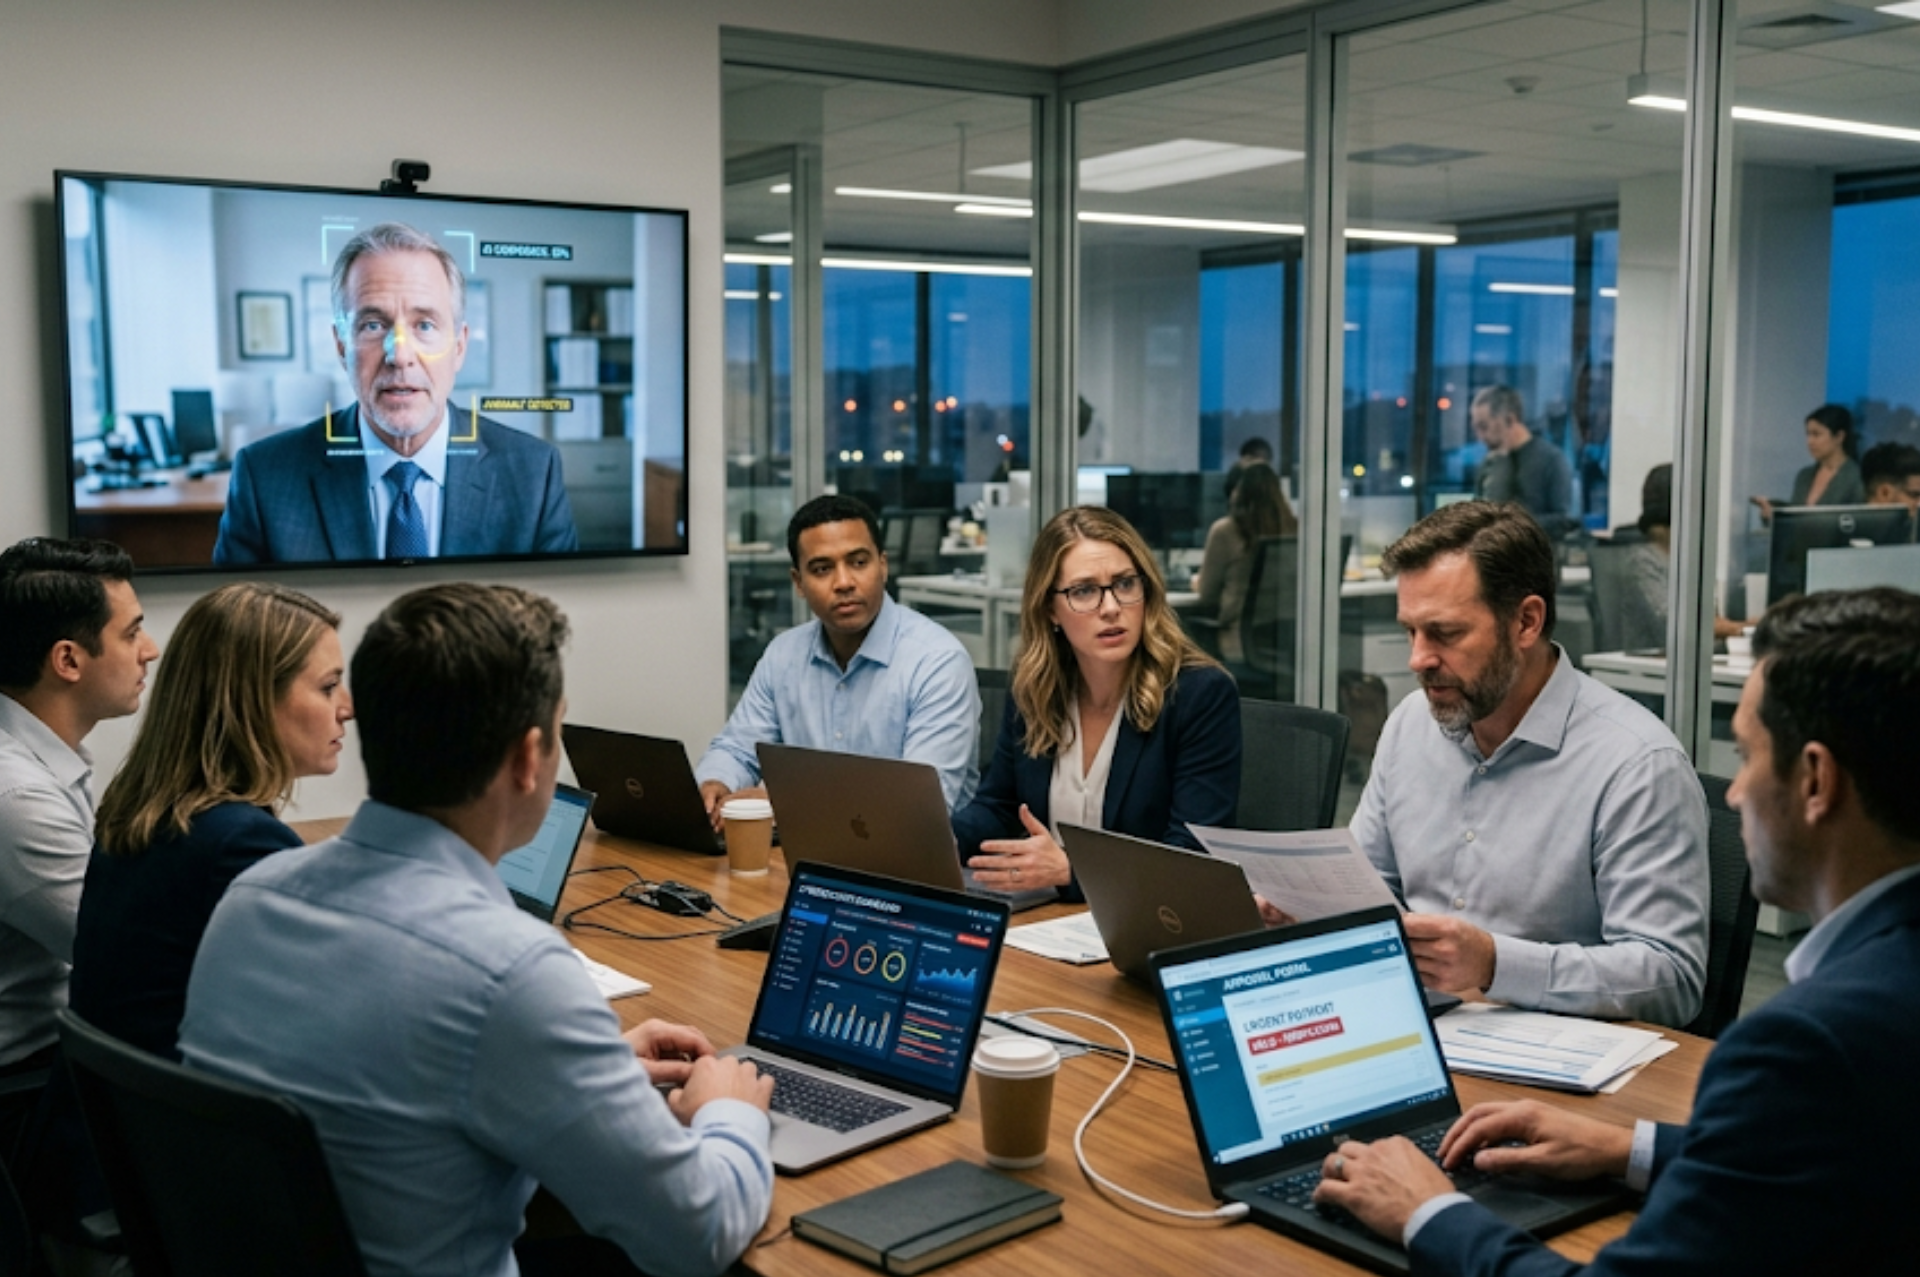
A modern deepfake CEO fraud attack often looks like this. An employee receives:
- A Teams or Zoom call from someone who looks and sounds like the CEO
- An urgent request tied to a confidential acquisition or payment
- Pressure to move quickly and avoid involving others
The employee complies because everything appears legitimate. The voice sounds right. The face looks real. The context feels believable. By the time the fraud is discovered, the funds are gone.
Why These Attacks Are Increasing
The barrier to entry has collapsed. Voice cloning software now requires only a few seconds of public audio to generate a convincing impersonation. Public webinars, podcasts, LinkedIn videos, earnings calls, and social clips provide attackers with more than enough material.
At the same time, business email compromise AI attacks have become significantly harder to detect because AI-generated communication no longer contains the grammar issues or awkward phrasing that once raised suspicion.
The result is a new category of fraud where:
- Social engineering is automated
- Executive impersonation is scalable
- Verification habits are outdated
The Warning Signs Most Employees Miss
Unusual Urgency Around Payments
Deepfake fraud almost always introduces urgency early. The request must happen immediately, is confidential, and should avoid standard approval processes. That pressure is intentional. It prevents verification.
Requests That Bypass Existing Process
A legitimate executive may occasionally escalate something quickly. But legitimate leaders rarely ask employees to ignore finance controls, multi-person approvals, or standard vendor verification procedures. Fraud attacks specifically target process bypasses because process is what stops them.
Slight Audio or Video Inconsistencies
Deepfake technology is improving rapidly, but subtle issues still appear: delayed lip synchronization, unnatural pauses, flat vocal emotion, slight audio distortion, poor eye tracking. Employees trained to notice behavioral anomalies often detect attacks faster than employees trained only on technical indicators.
Communication Outside Normal Channels
A sudden request through a personal phone number, a new messaging app, an unfamiliar email domain, or an unscheduled video call should always trigger secondary verification, especially for financial requests.
Why Traditional Security Awareness Training Fails Here
Most awareness training was designed for older phishing models. It taught employees to look for misspellings, suspicious links, bad grammar, and generic greetings. AI-generated fraud removes many of those indicators.
Modern voice cloning scam campaigns succeed because they exploit trust rather than technical weakness. That means the defense strategy must shift from “spot the fake” to “verify the request.”
Wire Transfer Fraud Prevention Now Requires Process Controls
Technology helps. Process matters more. The organizations reducing exposure to deepfake CEO fraud are implementing:
- Multi-person payment approvals
- Out-of-band verification procedures
- Mandatory callback confirmation
- Financial escalation controls
- Restricted emergency payment authority
The most effective wire transfer fraud prevention strategy is simple: no executive request overrides verification.
Where AI-Driven Business Email Compromise Gets Dangerous
The biggest misconception is that these attacks only target large enterprises. SMBs are often more vulnerable because approval chains are smaller, teams move faster, verification is more informal, and executives are more accessible publicly. Attackers know this. An SMB with weaker controls and high operational trust is often easier to exploit than a heavily regulated enterprise.
The Role of Incident Response and Digital Forensics
Once a fraudulent transfer occurs, speed matters. An effective incident response and digital forensics process helps organizations preserve evidence, trace communication activity, determine attack origin, support recovery efforts, and reduce ongoing exposure.
But the reality is simple: prevention is significantly cheaper than post-incident recovery.
What a Defensible Fraud Prevention Strategy Looks Like
Organizations handling these threats well usually have strong financial approval controls, executive impersonation procedures, updated employee training, secure communication workflows, and incident response planning. They assume AI-generated fraud attempts will happen, because they already are.
Final Thought
Deepfake CEO fraud works because it targets human trust at the exact moment process gets ignored. The organizations most exposed are not necessarily the least technical. They’re the ones relying on assumptions instead of verification.
Defensible works with growing organizations to strengthen fraud prevention controls, investigate AI-driven attacks, and reduce operational exposure before incidents escalate.
Think your organization could spot a deepfake fraud attempt today? Start by reviewing the processes attackers expect you to skip. Talk to an expert.